A dental software user access review is a regular check of who still needs each permission, with a recorded decision to keep, reduce, expand or remove it. In ProDent, user permissions control who can enter each area, but the clinic still has to decide which access fits each responsibility. A periodic review keeps that decision current as people and tasks change.
Take a common case: someone needs to cover billing for a few days. Which access should they get, for how long and who will check that it's removed afterward? The answer shouldn't depend on improvisation.
The decision affects much more than security. Permission that's too broad can expose information and allow unnecessary changes. Permission that's too narrow can push the team toward shared logins, informal requests and incomplete records. At either extreme, the manager loses traceability and makes decisions about scheduling, financials, inventory, CRM or KPIs with less confidence.
The most useful approach is to treat users and permissions as a management routine. Instead of setting them up once and forgetting them, the clinic reviews access as the work changes, documents temporary exceptions and confirms that each person can do what they need without seeing or changing what isn't part of their job.
The problem isn't only too much access
Access control usually comes up when there's a security question or when someone needs to find out who did something. But a good setup also protects the flow of work. The front desk needs to run the schedule and patient communication. The clinical team needs the information required for care. Billing needs to record and reconcile transactions. Management needs to track results and investigate discrepancies.
That doesn't mean everyone in a department should have the same permissions. Two front desk team members may have different responsibilities. One may manage the schedule, while the other also follows up on treatment opportunities or helps with collections. Job title is a starting point, but the real task is the more useful criterion for setting access.
The goal is sufficient access. It lets each person carry out the agreed responsibility, keeps every action tied to its author and cuts down on workarounds. That combination improves operations and the quality of the data that reaches management.
Knowing who changed each piece of information, when the change happened and which user made it strengthens the clinic's operational and legal footing. Traceability helps investigate discrepancies, fix processes, preserve individual accountability and show that access to personal and clinical data is controlled. In information security, access control combines authentication, authorization and auditing, and auditing is the part that records what each user did. That history doesn't eliminate risk or replace legal advice, but it provides important evidence to clarify incidents, review permissions and demonstrate good data protection clinics.
Access recertification is a management decision
Recertifying access means reviewing who still needs each permission and recording the decision to keep, reduce, expand or remove it. You don't have to wait for someone to leave or for a problem to appear. The review can be part of the clinic's routine whenever there's a role change, vacation coverage, a reorganization, a new process or a question about a change in the system.
How often you review should match your size, turnover and complexity. A small clinic can review users at set points on its management calendar. An operation with more locations, providers or shifting responsibilities may need a shorter cycle. What matters is having an owner, a criterion and a next review date.
The core question for every review: Does this person need to see, edit or approve this information to carry out a current responsibility?
The see, edit, approve test
See
Viewing access should be tied to a concrete need. Someone who checks the schedule to guide a patient may not need detailed financial information. Someone who tracks management results may need a consolidated view, but not necessarily the ability to change entries. Ask which decision or task depends on that information.
Edit
Editing requires responsibility for the quality of the record. Does the person know when to make an entry, which field to use and how to correct a mistake? Is there enough training to avoid notes in the wrong place, duplicates or improper deletions? A technical permission only works well when the process is clear too.
Approve
Approving is a management responsibility, even when the workflow has no button with that name. The clinic needs to define who signs off on discounts, billing exceptions, adjustments, sensitive patient profiles or rule changes. This question separates doing from deciding and keeps convenience from turning into permanent authorization.
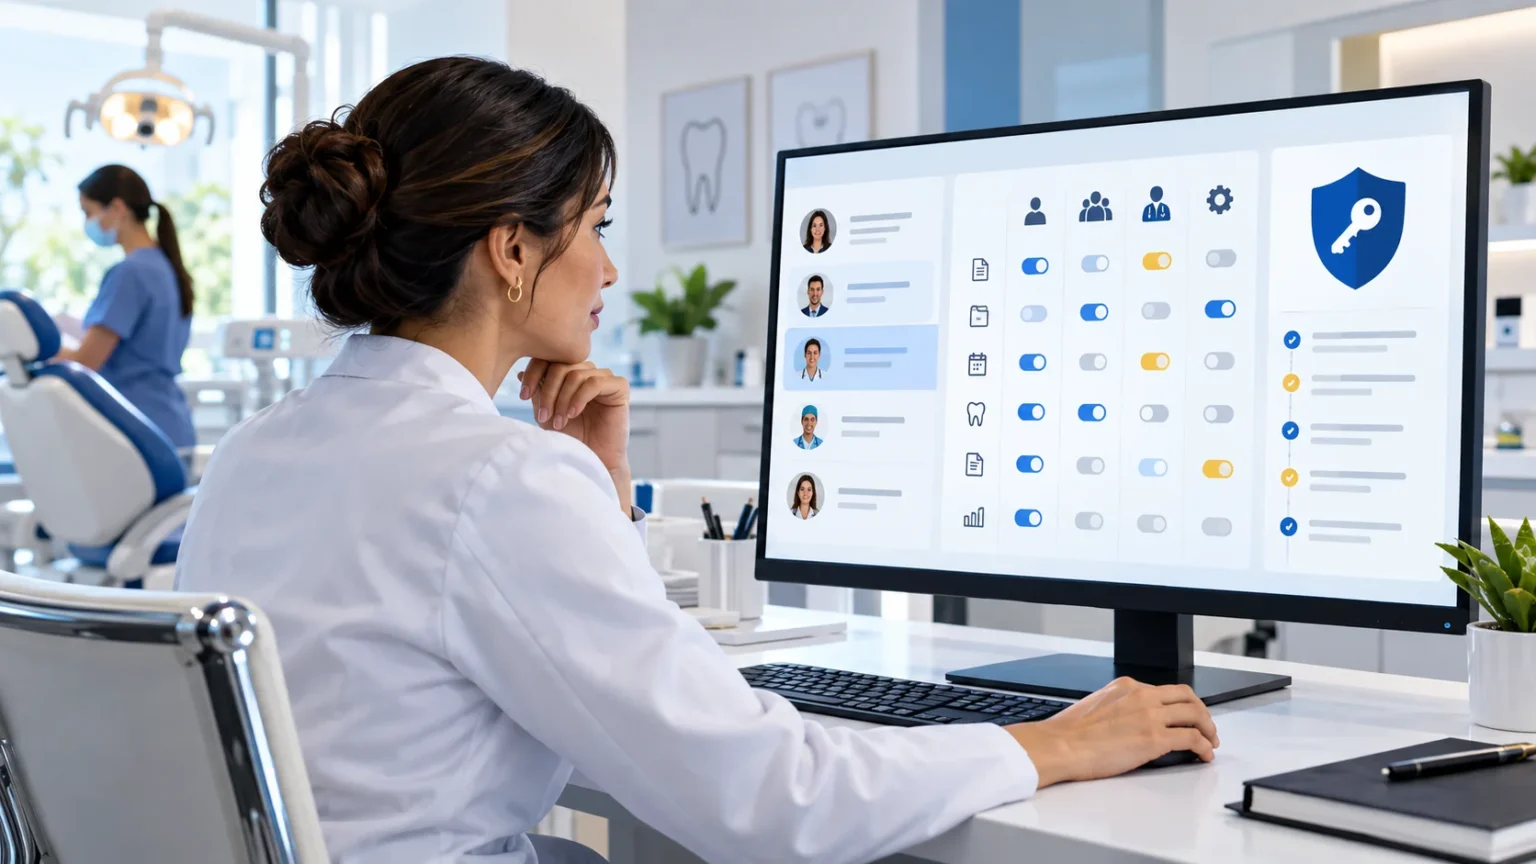
ProDent organizes users by individual identification, department and permission style, which is the level of permission that sets what each user can access and edit. The clinic uses that structure to reflect its real responsibilities. Not every conceptual split between seeing, editing and approving maps to a granular setting in every area, so confirm the final design in the system and, when needed, with the support team.
A playbook for reviewing user permissions in ProDent
1. List active users and their current responsibilities
Start with people, not screens. Confirm each user's individual name, department, current role and the activities they actually perform. Look for accounts belonging to people who have left, generic logins and access kept only because "it's always been that way." Individual users make it easier to identify who did what and reduce reliance on memory when questions come up.
2. Pick the most sensitive workflows
Don't try to review the whole system at once. Prioritize areas where a change affects patient care, privacy, cash flow or management reporting. Scheduling, patient records, documents, financials, inventory, CRM and KPIs can be reviewed in an order the clinic sets. For each workflow, describe what needs to be seen, recorded, corrected and approved.
3. Compare access with real tasks
Talk with department leads and with the people doing the work. A permission that looks excessive may be supporting a legitimate task that was never formalized. A permission that looks right may be insufficient and lead to password requests or side controls. The review needs to reveal the process before deciding the configuration.
4. Treat exceptions as temporary
Vacation coverage, the absence of a key person, a reconciliation push or support between locations may require extra access. Record the reason, the person, the area, the start date, the review date and who approved it. Don't assume the system ends the permission automatically. Removing it has to go on the calendar of whoever manages users.
5. Validate the operation after the change
After reducing or expanding a permission, confirm the person can still do the task without a shared login, rework or delays. Also check whether the history lets you reconstruct relevant actions. If the change raises questions or blocks a legitimate routine, use support to review the configuration and the training.
What ProDent organizes and what stays with the clinic
In user setup, ProDent lets you organize each user's individual name, department and permission style. That foundation helps limit what each person can access and edit, and it supports identifying who performed actions or changes where traceability is available in the workflow you're reviewing.
The system provides structure. The clinic remains responsible for defining roles, authorizing access, protecting credentials, guiding the team, reviewing changes and investigating the context of each incident. Management also has to confirm that clinical information stays in the right fields and that financial data, documents and KPIs are accessed only as the work requires.
This division avoids a dangerous expectation: that setting up users once solves governance. Consistent permissions depend on consistent processes. If nobody knows who records a payment, approves a discount or fixes a patient profile, the screen just reproduces the ambiguity of the routine.
Signs the review can't wait
- Two or more people use the same login
- Former employees' accounts are still active after team changes
- The clinic can't identify who made a significant change
- Temporary access remains with no review date
- Team members ask for someone else's credentials to finish tasks
- Information goes unrecorded because access doesn't match the responsibility
- Everyone in a department has the same permissions despite different tasks
- The manager gets inconsistent KPIs and can't find where the process broke down
On their own, these signs don't prove the configuration is wrong. They show the clinic needs to compare access, responsibility, training and process quality.
How user permissions affect your management numbers
User permissions also shape how much you can trust the numbers. If untrained people can change sensitive entries, data consistency is exposed. If the person doing the task can't record it at the right moment, the system receives information that's late, incomplete or outside the workflow.
That's why a recertification meeting shouldn't end with just a list of users. It needs to show where record quality improved or got worse after a change. Management can watch signals such as how many exceptions are still open, whether shared accounts exist, recurring corrections, delays caused by blocked access and difficulty reconstructing an action.
These are suggested controls for the clinic's routine, not built-in ProDent metrics. Their value lies in using evidence from the work to decide whether the permission, the process or the training needs to change.
Support and training are part of access control
When the team doesn't understand the purpose of a restriction, they tend to see the permission as an obstacle. Short training tied to the task helps explain what should be recorded, who is responsible for the information and when to ask for an adjustment. That reduces improvisation and makes individual logins stick.
HartSystem's human support and personalized consulting can help review the configuration in the context of your clinic. To make the conversation productive, bring one role, three frequent tasks, one temporary exception and one traceability question. That way, the guidance starts from real work, not an abstract list of screens.
The right access improves security and management
User permissions in ProDent aren't just for locking areas of the system. They help align task, responsibility and authorship. When the clinic reviews access, controls exceptions and validates operations after each change, it protects information without blocking the team and increases confidence in the records management relies on.
Pick one sensitive workflow, define who needs to see, edit or approve and record exceptions with a review date. With Pro365 GO, the new ProDent that runs 100% on the web, every user has individual access you can review as your team changes. Book a demo and bring that access map to walk through a real case with our team.