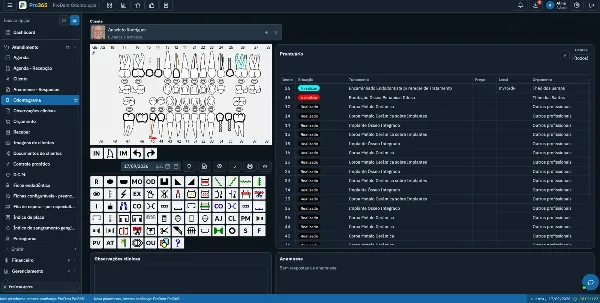
Role-based access in dental software means each user gets the access their job requires, and that access changes as the person's role changes. In ProDent, you register individual users, assign them to a department and set a permission style that defines what they can see and edit. To keep it right, review access at four moments in the user lifecycle: onboarding, role changes, temporary coverage and offboarding.
Picture this: at 5:40 p.m., the front desk finds a payment that was changed. The amount doesn't match what was agreed, the day's schedule is wrapping up and three people touched the patient's account. The question sounds simple: who made the change? When the team uses generic logins or overly broad permissions, the answer turns into an investigation based on memory.
That's when users and permissions stop looking like a technical setting. They become part of how the clinic is organized, because they define who can access each area, which person performed an action and where the process needs fixing.
ProDent lets you register users individually, link them to departments and set permission styles, which are the levels of permission that define what each profile can access and edit. That structure supports security, traceability and clear accountability, as long as the clinic configures access around the real work.
THE CORE IDEA
The best permission isn't the most open or the most restrictive. It's the one that lets a person do their job with enough autonomy and with exposure that matches their responsibility.
This follows the principle of least privilege, a widely recommended information security practice: each user should have only the permissions needed for their activities. The same clinic calls for avoiding shared accounts and passwords between team members.
Access should follow the role, not the convenience of the moment
In a dental clinic, scheduling, patient records, documents, financials, inventory, CRM and KPIs live in the same management system. That makes the work more integrated, but it also requires one direct question for every user: which information and actions does this person really need to do their job?
Opening everything may seem faster during setup, but it increases exposure and weakens the link between each action and its author. Restricting too much also causes problems, because the team may need approval for simple tasks or turn to messages, spreadsheets and loose notes as shortcuts.
A balanced setup starts with four basics:
- each person works with an individual, identifiable user
- the permission style matches the tasks they need to perform
- the department places the user within the team's workflow
- role changes trigger a new access review
The user lifecycle in four events
Permission reviews are often treated as a yearly task. In practice, access changes whenever the team changes. Four events deserve a clear procedure.
- A new team member joins
Before their first login, list the tasks of the role, identify the areas they need and set the right permission style. Register the user individually, assign the correct department and test a real task. The goal is to confirm the person can work without receiving access they don't need.
- A change in role or responsibility
A promotion, a move to another department or new duties may require new permissions. The review should look at what needs to be added and what no longer makes sense. Adding access without removing old permissions makes the profile grow indefinitely.
- Temporary coverage
Vacations, absences and busy periods may lead someone else to take on part of the routine. Define which tasks will be covered, which access is essential and when the review has to happen. If the system doesn't apply an automatic expiration for the configuration your clinic uses, record the return date and who is responsible for reviewing the profile.
- Offboarding or the end of the need
Access should be reviewed as soon as someone leaves the team or no longer needs a given area. Besides removing or adjusting the permission, management has to reassign open tasks, pending contacts and operational responsibilities so no process is left without an owner.
Access map by role: a starting point
The map below doesn't replace a configuration tailored to your clinic. It's meant to start the conversation between management, department leads and the support team.
| Role | Typical need | Watch out for |
|---|---|---|
| Front desk | Scheduling, patient registration, confirmations, check-in and follow-ups tied to patient visits | Broad financial data, structural settings and clinical information with no operational need |
| Clinical team | Patient records, dental charting, images, forms, documents and care-related records | Administrative settings and financial views that aren't part of their responsibility |
| Billing | Payments received and made, overdue accounts, associate payouts and the reports they need | Clinical changes and settings unrelated to the financial close |
| Management | KPIs, audit, operational oversight and settings that fit the role | Broad access with no review, shared credentials and routine work done under a generic profile |
The exact permissions available may vary by version, environment and configuration. Validate the design with the support team before changing sensitive areas.
How to use traceability to fix the process
Back to the changed payment from the start of this article. Traceability isn't just for finding a person. It helps reconstruct the event and turn a failure into operational learning.
When there's an error or a question, investigate in this order:
- which patient profile, document, entry or status was changed
- on what date and at what time the action happened
- which user was associated with the recorded action
- which rule or guideline the person should have followed at that moment
- whether the problem was inappropriate access, insufficient training or an ambiguous process
- which correction the record needs and which prevention step goes into the routine
This sequence avoids two weak responses. The first is blaming someone before understanding the workflow. The second is fixing only the data and leaving untouched the condition that caused the error.
TRACEABILITY WITH A PURPOSE
The action history is most useful when it guides correction, training and process improvement. The clinic should preserve individual accountability without turning audit into punitive surveillance.
Signs of too much access
- more than one person uses the same user
- team members can view areas unrelated to their tasks
- significant changes appear with no clear author
- former employees' accounts stay active after team changes
- a team member's profile keeps permissions from previous roles
Signs of too little access
- simple tasks depend on someone else every day
- the team records information outside the system to keep moving
- users borrow credentials to finish a task
- the person responsible for a step can see the data but can't take the action required
- patient service stops because the profile didn't keep up with a change in responsibility
Both extremes hurt efficiency. The goal of the review isn't to cut access at any cost. It's to align access, responsibility and routine.
Review one role in 30 minutes
Instead of reviewing the whole clinic at once, choose one critical role, such as front desk or billing, and run a short session with the person who does the work.
- List five real tasks
Use activities from the past week, not a generic job description.
- Mark the areas used
Identify what the person needs to view, add, change and track to complete each task.
- Compare with the current profile
Look for access that's missing, excessive or inherited from a previous role.
- Test a complete case
Run a common task from start to finish and confirm the author shows up clearly in the related workflow.
- Record the decision and the owner
Note what will be kept, changed or validated with support, who will make the adjustment and when access will be reviewed again.
Where support makes a difference
Management knows the roles, the risks and the internal agreements. The support team knows how ProDent's configuration works and can guide the right use of the permission styles, users and departments available in your clinic's environment. Combining those two perspectives avoids trial-and-error decisions.
Support is also valuable during implementation, growth and department reorganization. Training based on real situations helps each team member understand why the permission exists and which responsibility comes with the access. The system organizes users and traceability, while the clinic defines roles, reviews changes, guides the team and protects individual credentials.
Role-based access that grows with your clinic
When the clinic hires providers, creates departments, extends hours or spreads work across locations, access has to change too. With individual users, consistent permission styles, organization by department and traceability, ProDent helps clarify who does what, give autonomy that matches responsibility and investigate deviations based on facts.
Choose one critical role, list five real tasks and compare what the work requires with the current access. With Pro365 GO, the new ProDent that runs 100% on the web, you can set and adjust access as each person's role changes. Book a demo to see users and permissions applied to your clinic's routine.